Review and manage Firewall Threat Defense migration job
Use this task to effectively monitor and manage Firewall Threat Defense migration jobs, track device migration progress, handle evaluation period activities, and resolve deployment or identity policy issues that may arise during the migration process.
The migration dashboard provides the status of all migration jobs initiated from the Security Cloud Control. You can expand a specific job to see the status of individual devices associated with that tenant. This helps you keep track of the progress of your migration and identify issues, if any, that need to be addressed.
When a migration job is successful, you have 14 days to test and assess migration changes. If you are convinced about the migration changes, we recommend that you commit the devices manually, and not wait for Security Cloud Control to automatically commit the migration changes.
Procedure
Step 1 | Check migration job status in the migration dashboard. If you have set up alerts for device workflows, click the notifications icon Review the following information for each migration job:
| ||||
Step 2 | Manage migration job actions using the Actions menu. Click
| ||||
Step 3 | Monitor deployment status and address validation issues. After a successful migration, Security Cloud Control deploys the configuration to the device. If the system identifies errors or warnings in the changes to be deployed, it displays them in the Validation Messages window. To view complete details, click the arrow icon before the warnings or errors. If the deployment fails, see the Best Practices for Deploying Configuration Changes section of Firepower Management Center Device Configuration Guide X.Y. | ||||
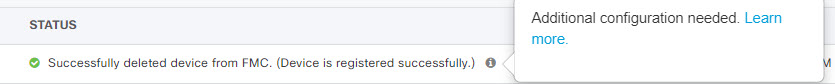
Step 4 | Configure realm sequence for identity policy if required. If the device contains an identity policy with a Realm or ISE configuration, configure your device as a proxy for Security Cloud Control to communicate with the identity source. The identity policies don't function if Security Cloud Control fails to connect to the Identity Realms. A tooltip appears in the Status column for a device that requires additional configuration.
| ||||
Step 5 | Commit migration changes if satisfied with the evaluation. When a job is completed successfully, the FTD Migration job is successful message appears in the Status column. You can click the tooltip to see the number of days remaining for evaluating the manager. You can click Commit Migration Changes to commit the changes manually before the 14 days evaluation period ends.
|
 to see the alerts that have been triggered during the migration process. Additionally, if you have opted to receive email notifications from
 to execute the following actions:
You have successfully reviewed and managed the Firewall Threat Defense migration job. The migration status is monitored, any deployment issues are addressed, identity policy configurations are updated as needed, and migration changes are committed or cancelled based on your evaluation.
Note that for the On-Premises Firewall Management Center 1000/2500/4500, you would have migrated devices from Version 7.4, which is unsupported for general operations. To return the On-Premises Firewall Management Center to a supported version you must remove the re-migrated devices, reimage back to Version 7.2.x, restore from backup, and re-register the devices.